Vanta
Automates the evidence collection behind security compliance
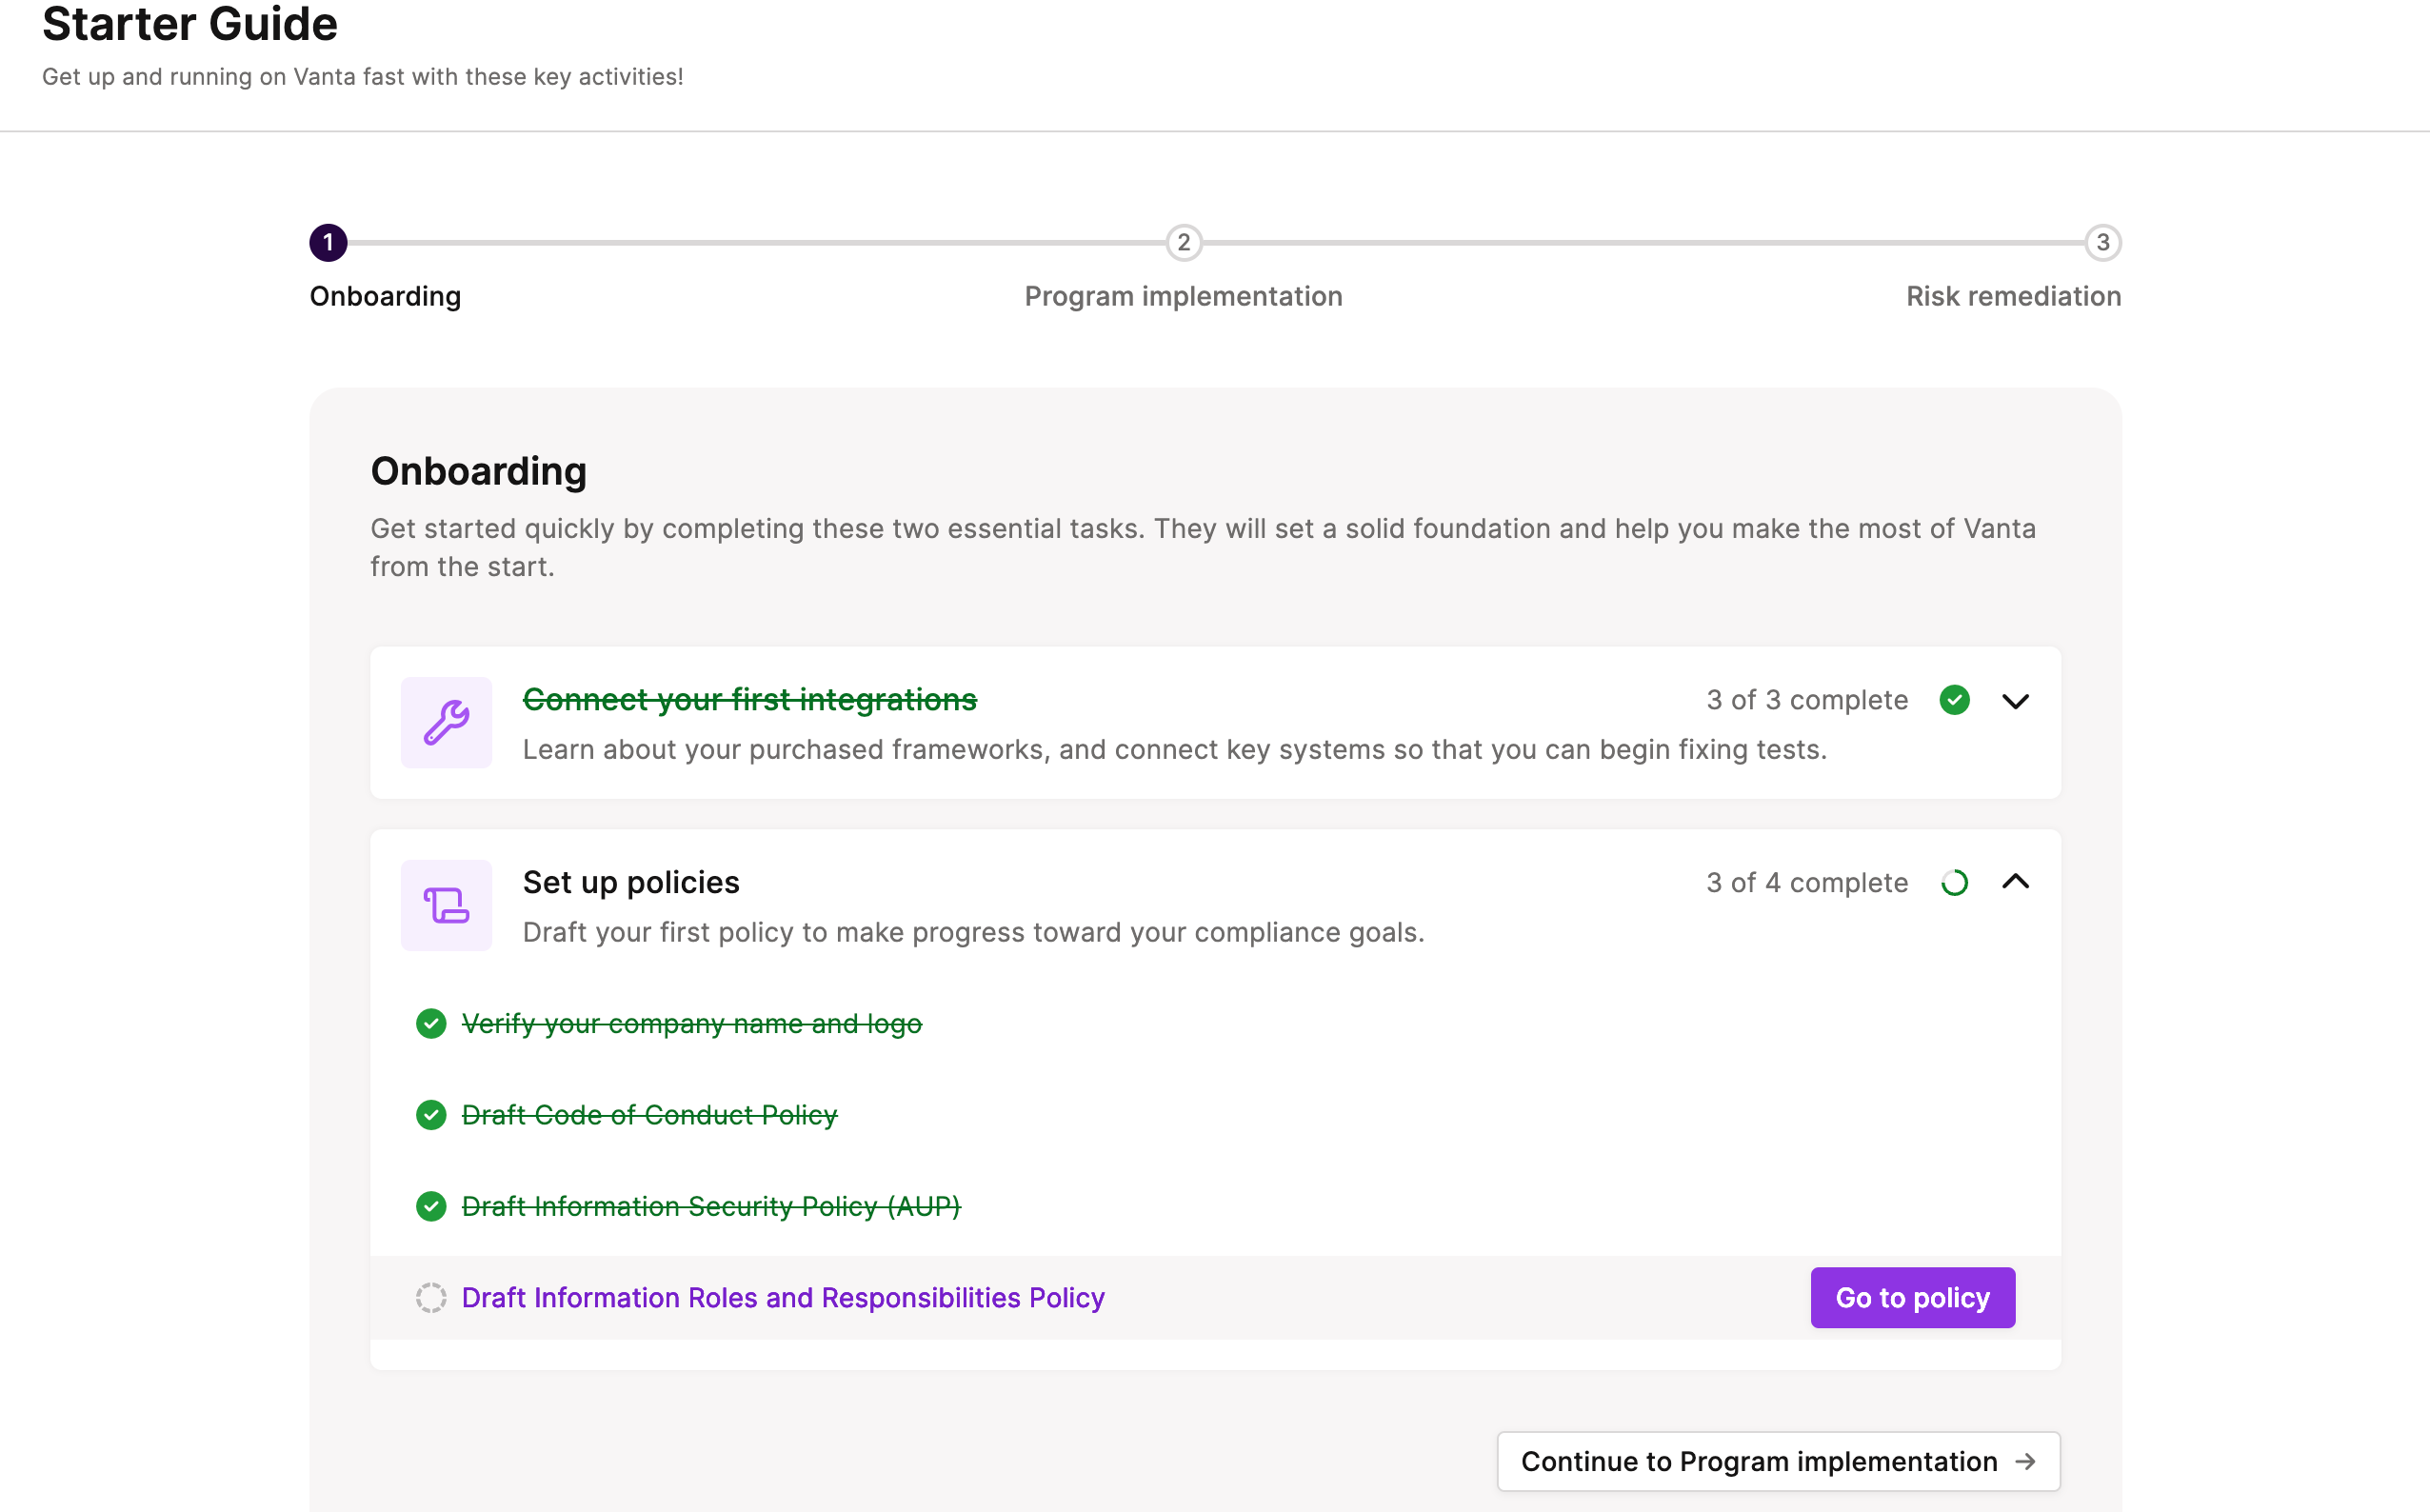
Vanta is for companies that have to prove their security to customers and auditors. It connects to the tools a company already runs - more than 400 integrations across cloud, identity, device management and code - and continuously checks the controls behind a framework, collecting the evidence rather than asking someone to screenshot it once a year. Frameworks covered include SOC 2, ISO 27001, GDPR, HIPAA, HITRUST, ISO 42001 and the NIST AI Risk Management Framework, along with custom frameworks of your own. Around that sit personnel and access reviews, risk management, vendor and third-party risk, and questionnaire automation that drafts answers to the security reviews prospects send. A Trust Center publishes your posture as a public page so buyers can check it themselves, and audits run through partner auditors with evidence already gathered. Pricing is quoted rather than published, and scales with company size and the frameworks in scope.
- 400+ integrations pull evidence from the tools you run
- Continuous control monitoring rather than annual checks
- SOC 2, ISO 27001, GDPR, HIPAA and HITRUST frameworks
- ISO 42001 and NIST AI Risk Management for AI governance
- Custom frameworks alongside the standard ones
- Access reviews, risk management and vendor risk
- Questionnaire automation drafts security review answers
- Trust Center publishes your posture for buyers to check
What people are saying about Vanta
50% neutral“Oh yeah I think Vanta is as good as any on the market. Enterprise scale maybe look at hyperproof or drata as well but they should be roughly on feature parity at this point.”
“I'm looking to onboard a tool to enable CCM, Vanta being one option, so this stood out to me.”
“On the surface it looks decently comprehensive, bringing a ton of different aspects into one platform for oversight, but it’s my first time using it and I haven’t throughly explored it yet.”
“Vanta is a beautiful product.”
“Vanta or Scytale for SOC 2 and ISO 27001? The feature lists have converged - the real split is whether you run compliance yourself or want a platform plus a dedicated GRC expert.”
“Wedge: win where filter-based tools structurally fail, get real KPIs, then get compliant and go upmarket (Vanta/Rippling-type buyers) where a giant static list is useless to them and Clay becomes the real fight, not ZoomInfo.”
“Thank you to Advantage Partners and Vanta for supporting us throughout the process.”
“It wouldn't automatically collect evidence from every external system the way platforms like Vanta do, but if that isn't the part you need, it may be worth a look.”
“At 30 people I would skip Vanta entirely and do two things. Export the logs you care about on a schedule to a folder you keep, and write the four or five policies you'd be asked for once, dated and signed.”
“I keep seeing tools like Vanta, Drata and OneTrust but they are to expensive for under 200+ people companies”
“Vanta publishes 65 AI agent controls for the gaps ISO leaves open”
“* It's quite expensive.”